Latest
From Memory Corruption to RCE: Inside a PyTorch Model-Loading Exploit Chain
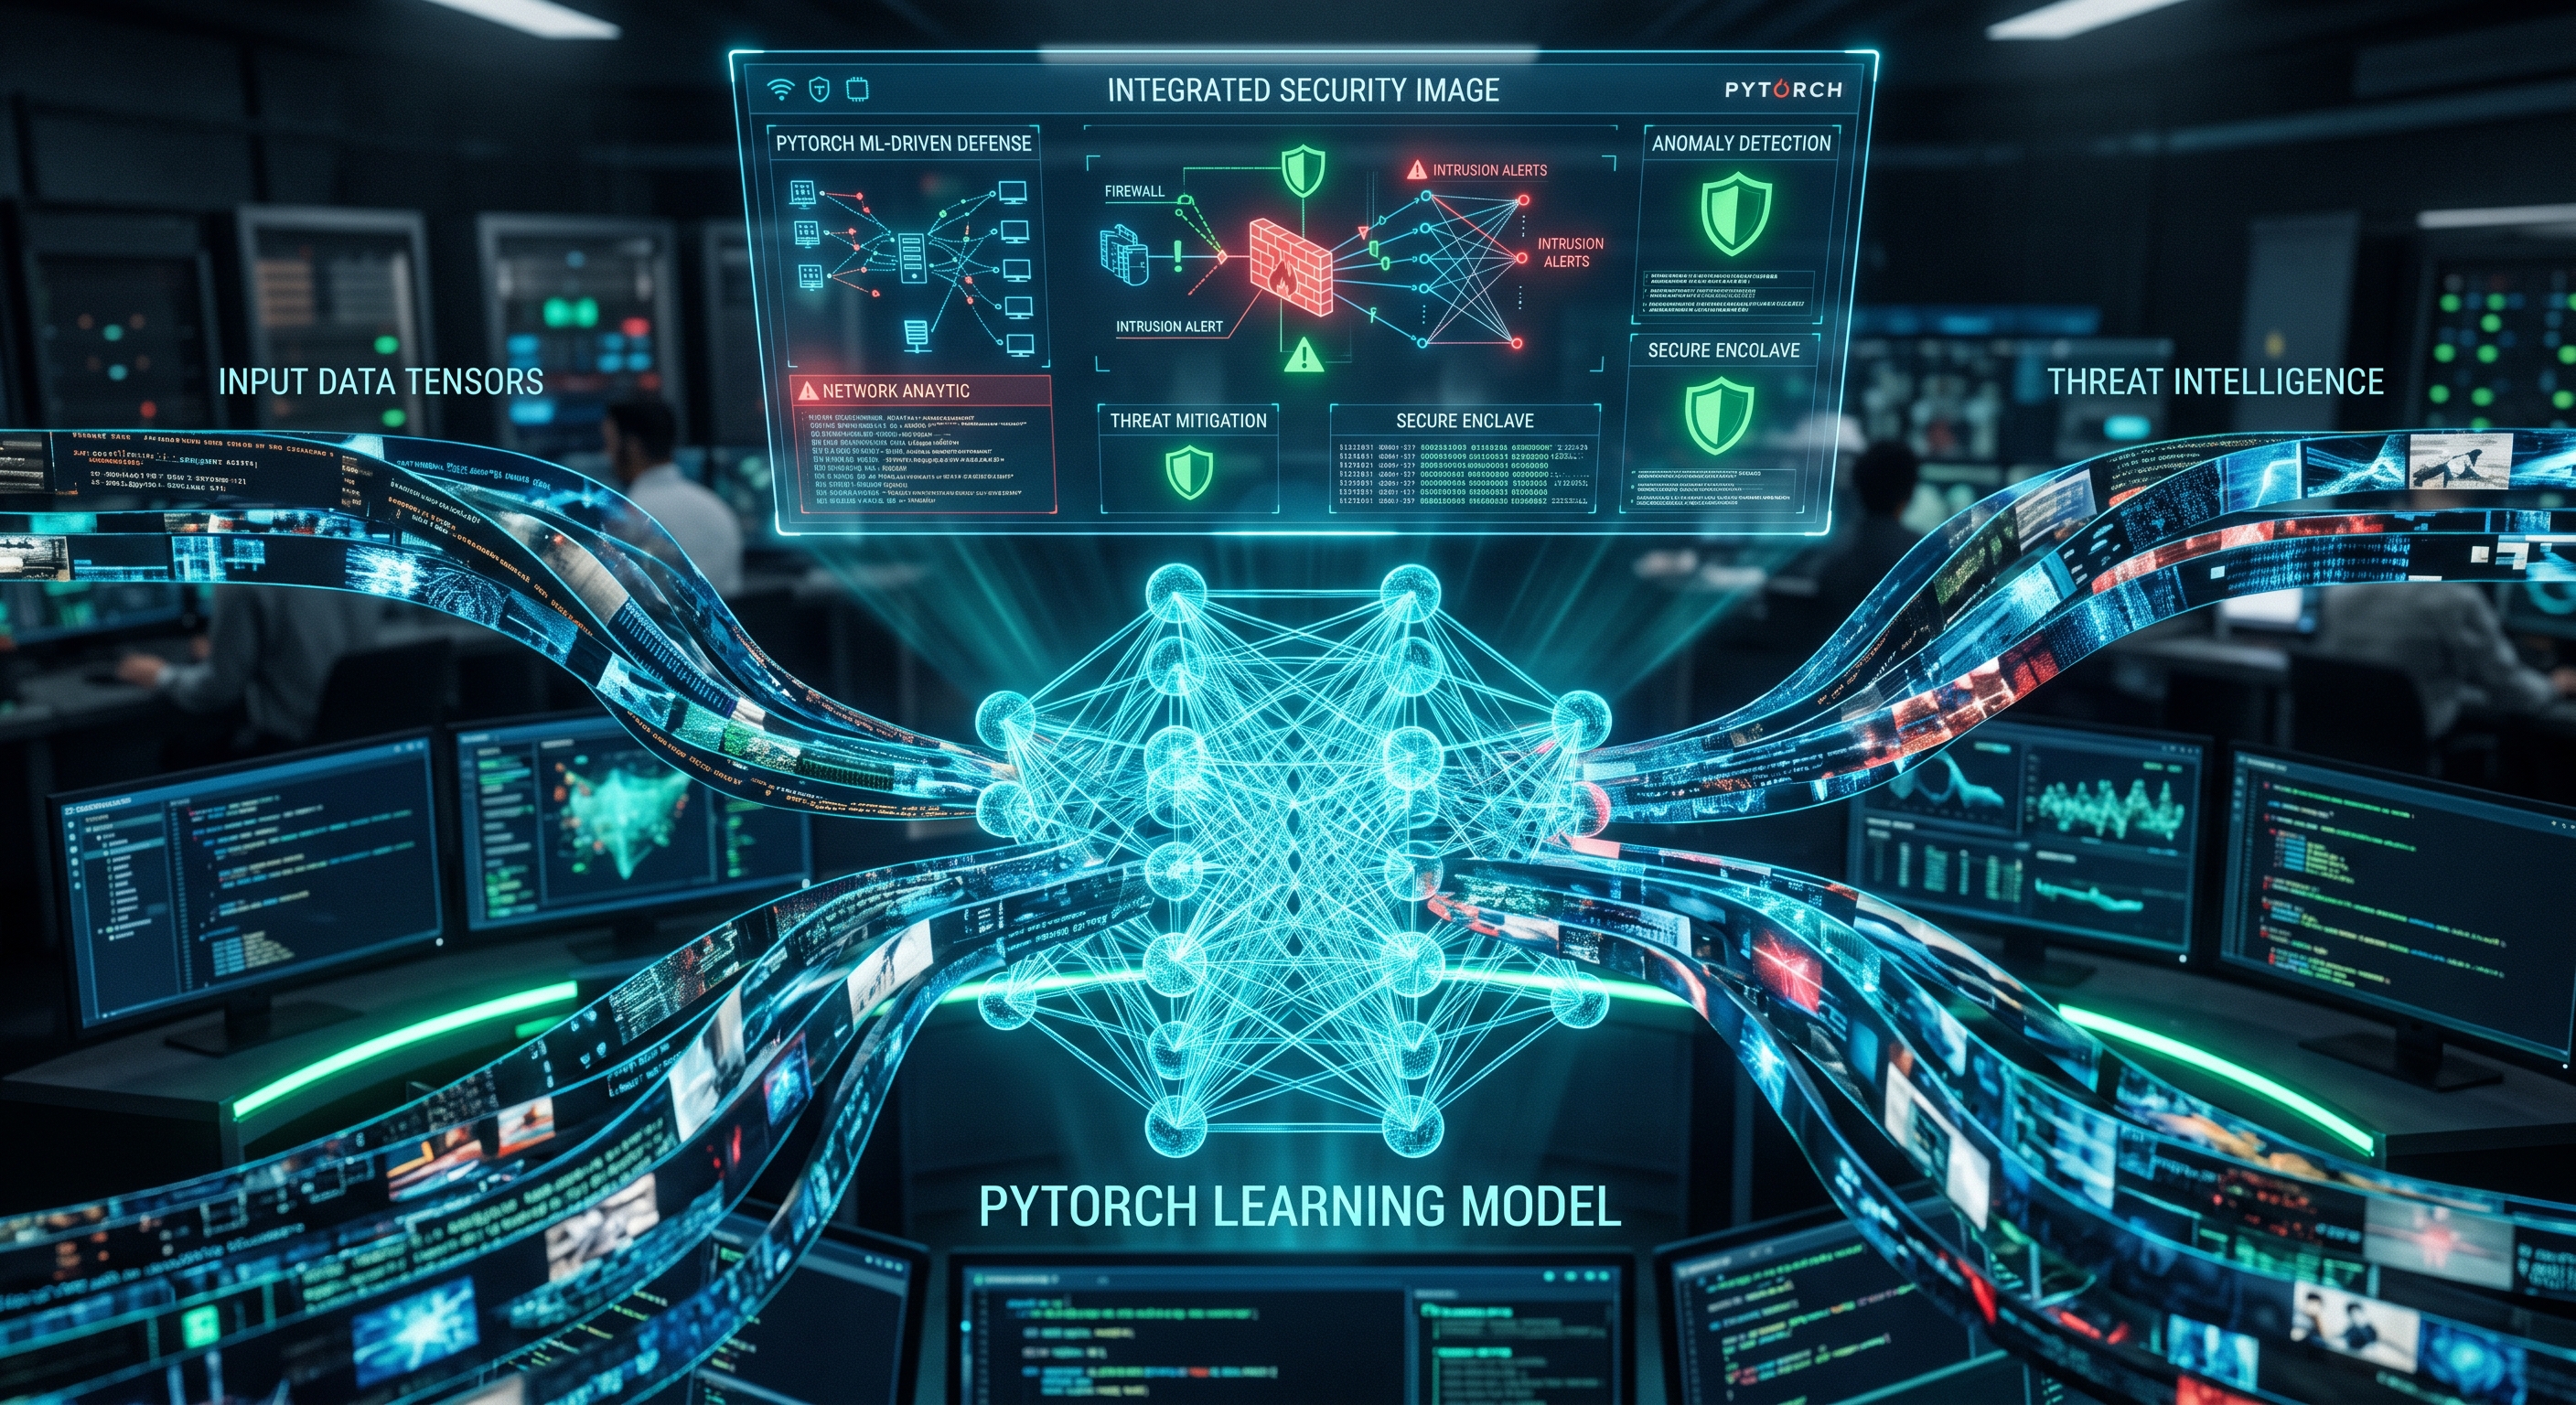
How a crafted PyTorch model can move from a model-loading bug to memory corruption—and potentially remote code execution in an AI application.
Intlix Blog
Research and engineering notes on AI systems, security, and the infrastructure that runs them — written by the people building it.

Latest
How a crafted PyTorch model can move from a model-loading bug to memory corruption—and potentially remote code execution in an AI application.

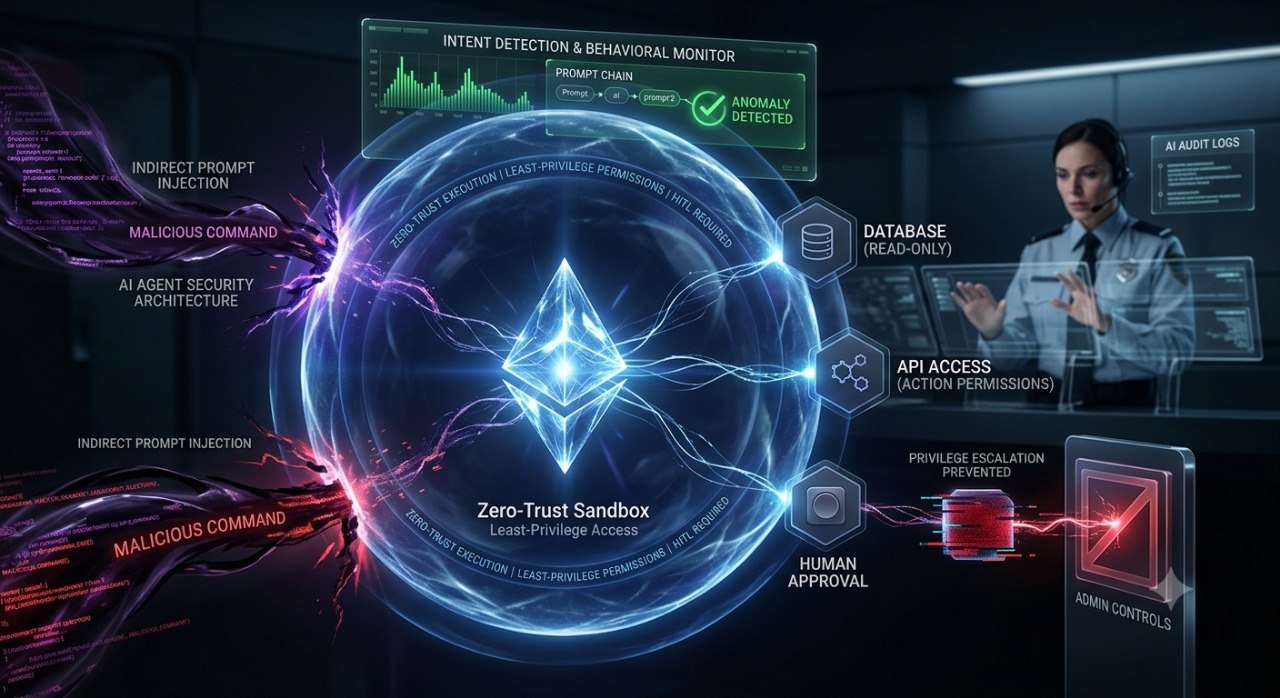
Learn how to secure the Agentic Security Stack. We explore three critical layers of risk—untrusted context, hijacked reasoning loops, and privileged tool exploitation—and outline a defense-in-depth architecture for production AI agents.

Autonomous AI agents bring powerful capabilities, but also introduce critical new security risks. Learn how to architect a defense-in-depth strategy to secure your agentic workflows.
We build and secure AI systems for teams that need them in production. Tell us what you are working on.
Tell us what you are working on, and we will show you where to start.
Talk to us